ESP-TEE: Espressif Just Gave the ESP32 a Real Trusted Execution Environment
Espressif's new ESP-TEE framework brings hardware-isolated secure storage, attestation, and rollback-safe OTA to the RISC-V ESP32-C6 — a serious security upgrade for a chip family that used to rely on trust, not isolation.
If you have ever built anything with an ESP32, you already know the tradeoff: incredible price-to-performance for Wi-Fi and Bluetooth connected projects, but historically pretty thin hardware security guarantees once your firmware is running. Secure Boot and flash encryption protected the boot chain, but once your application code was executing, a single bug anywhere in that application could expose your Wi-Fi credentials, TLS private keys, or device identity secrets sitting in the same memory space. Espressif's newer ESP-TEE (Trusted Execution Environment) framework, built for the RISC-V based ESP32-C6, changes that story in a way that is worth understanding whether you are prototyping a hobby sensor or evaluating IoT hardware for a production fleet.
What ESP-TEE Actually Is
ESP-TEE splits the chip into two worlds that run side by side on the same silicon: a Trusted Execution Environment (TEE) and a Rich Execution Environment (REE). The REE is where your normal FreeRTOS-based ESP-IDF application lives — your sensor loop, your MQTT client, your Wi-Fi stack. The TEE is a much smaller, isolated secure subsystem that handles only the sensitive operations: cryptographic signing, key storage, firmware verification, and attestation. Critically, this is not a software convention that a buggy application can accidentally violate — it is enforced by the RISC-V core's hardware privilege levels.
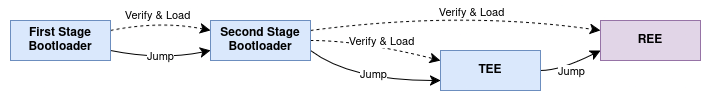
Figure: ESP-TEE secure boot flow — each bootloader stage verifies and loads the next before control jumps into the TEE or REE. (Source: Espressif ESP-IDF documentation)
Machine Mode vs. User Mode
The ESP32-C6's RISC-V core supports two privilege levels: Machine (M) mode and User (U) mode. ESP-TEE runs in the higher-privilege M-mode, while your entire application — including ESP-IDF itself — runs in the lower-privilege U-mode. The framework leans on RISC-V's Physical Memory Protection (PMP) and Physical Memory Attributes (PMA) checker to carve up flash and RAM so the U-mode application literally cannot read or write the memory regions the TEE owns. If an attacker finds a memory-corruption bug in your application code, or in a dependency you pulled into your firmware, that exploit is now walled off from the secrets the TEE is protecting — the isolation is enforced by the memory controller, not by hoping your code has no bugs.
Secure Storage, Attestation, and Rollback-Safe OTA
In practice, ESP-TEE gives firmware developers three capabilities that used to require either a separate secure element chip or a lot of custom engineering:
- Secure storage — sensitive data is kept in an encrypted external flash partition that is completely inaccessible from the REE side, so a compromised application can't simply read out stored keys or credentials.
- Attestation — the device can produce a cryptographically signed, ECDSA-based token that makes verifiable claims about its identity and security state, which is exactly the primitive a cloud backend or commissioning process needs to confirm it's talking to a genuine, unmodified device rather than a cloned or tampered one.
- Secure OTA updates — the REE can still fetch firmware over whatever transport you like (HTTPS, MQTT, whatever your fleet already uses), but the TEE independently verifies and writes the update, with automatic rollback if verification or boot fails. That closes a classic IoT weak point where a compromised update pipeline could push unsigned or malicious firmware straight into the running application.
Why Matter and PSA Certified Level 2 Matter Here
Espressif has specifically demonstrated ESP-TEE protecting the two categories of keys that matter most in a Matter smart-home device: the Device Attestation Certificate (DAC) key programmed once in the factory to prove device authenticity during commissioning, and the Node Operational Certificate (NOC) key generated at runtime each time the device joins a new Matter fabric. Both are now generated and used inside the isolated TEE rather than sitting in general application memory — a meaningful hardening step for a protocol ecosystem that is trying to standardize how consumer smart-home devices prove who they are.
The framework also lines up with PSA Certified Level 2, an independent lab-evaluated security profile from Arm's PSA Certified scheme that verifies a chip's Root of Trust can resist scalable remote software attacks (not physical attacks — that's a higher certification tier). The ESP32-C6 became the first RISC-V MCU to reach PSA-L2, and ESP-TEE is a big part of how it gets there. For anyone specifying hardware for a product that needs to pass a security audit, meet emerging IoT regulations, or simply survive due diligence from a security-conscious customer, being built on a PSA-L2 certified root of trust is a much stronger answer than simply trusting your own firmware.
The Catch: RISC-V Only, For Now
The obvious limitation is that ESP-TEE is currently exclusive to Espressif's RISC-V line, starting with the ESP32-C6 — it is not available on the older Xtensa-based ESP32 and ESP32-S3 chips that most existing ESP32 projects and products are still built on. If you're maintaining a large existing fleet on those older chips, this doesn't retroactively help you; it's a reason to look at the C6 (or newer RISC-V parts following it) for new designs where key protection and attestation actually matter, such as anything handling payment data, access control, or being deployed at a scale where a single leaked signing key becomes a fleet-wide incident.
Why This Is Worth Paying Attention To
IoT security has historically been an afterthought bolted onto cheap, capable silicon after the fact — usually in the form of please-don't-hardcode-your-Wi-Fi-password style advice. ESP-TEE is Espressif building actual hardware-enforced isolation into one of the most widely used microcontroller families on the planet, at essentially no added bill-of-materials cost since it doesn't require a discrete secure element. For anyone working across IoT, embedded systems, or infrastructure security, it's a good template for what secure by design actually looks like at the silicon level, rather than as a marketing phrase.
Sources
- Announcing ESP-TEE Framework for ESP32-C6 — Espressif Developer Portal
- Building Hardware-Enforced Trust into Matter Devices with ESP-TEE — Espressif Developer Portal
- ESP-TEE: User Guide — ESP-IDF Programming Guide (ESP32-C6)
- Espressif's ESP32-C6: the World's First RISC-V MCU to Achieve PSA-L2
- PSA Certified Level 2 — PSA Certified
This article was researched and drafted with AI assistance as part of an experiment in building a faster tech-writing workflow, then reviewed and edited before publishing.
Keep Reading
Espressif's New ESP-TEE Already Has a 9.3-Severity Out-of-Bounds Write Bug
Espressif's Trusted Execution Environment for the ESP32-C5/C6/C61/H2 shipped with an unchecked-pointer bug (CVE-2026-45328, CVSS 9.3) that lets ordinary application code corrupt memory inside the very boundary the TEE exists to protect.
AI Agents Just Became Both the Weapon and the Target — What Every Infrastructure Team Needs to Know
A ransomware crew compressed a two-week breach into 10 hours using AI agents. Days later, CrowdStrike launched a product built to stop exactly that. Here's what changed and what to actually do about it.
The Vibe Coding Wake-Up Call: When Your AI Assistant Becomes the Attack Surface
A BBC reporter's laptop was compromised without a single click — through an AI coding platform called Orchids. No malicious download, no phishing link, no user error. This is what happens when AI agents get deep system access before anyone secures them properly.